F
licenseNot graded
qualityF
maintenanceA standalone server enabling Snyk security scanning through the Model Context Protocol, with support for repository and project analysis, token verification, and CLI integration.
15
-

The MCP SBOM Server is a tool that scans container images using Trivy to generate Software Bill of Materials (SBOMs) in both SPDX JSON and CycloneDX formats.
Container Image Scanning: Executes Trivy scans on specified container images
Multiple SBOM Formats: Supports both SPDX JSON and CycloneDX standards
MCP Integration: Operates as a server adhering to the Model Context Protocol (MCP)
Compatibility: Works with Python 3.12 and MCP 1.6
Debugging: Provides tools for debugging via MCP Inspector
Requirements: Needs uv, trivy, and Node.js for installation/execution
Windows Support: Includes guidance for Windows systems
Performs container and application vulnerability scanning using Trivy and produces a Software Bill of Materials (SBOM) in CycloneDX format.
Click on "Deploy Server".
Wait a few minutes for the server to deploy. Once ready, it will show a "Started" state.
In the chat, type @ followed by the MCP server name and your instructions, e.g., "@MCP SBOM Server scan my Dockerfile for vulnerabilities and generate an SBOM"
That's it! The server will respond to your query, and you can continue using it as needed.
Here is a step-by-step guide with screenshots.


MCP server to perform a Trivy scan and produce an SBOM in CycloneDX format.
Install the following.
Related MCP server: MCP NVD Server
"mcpServers": {
        "mcp-sbom": {
            "command": "uv",
            "args": [
                "--directory",
                "/path/to/mcp-sbom",
                "run",
                "mcp-sbom"
            ]
        }
}This project employsuv.
Synchronize dependencies and update the lockfile.
uv syncUse MCP Inspector.
Launch the MCP Inspector as follows:
npx @modelcontextprotocol/inspector uv --directory /path/to/mcp-sbom run mcp-sbom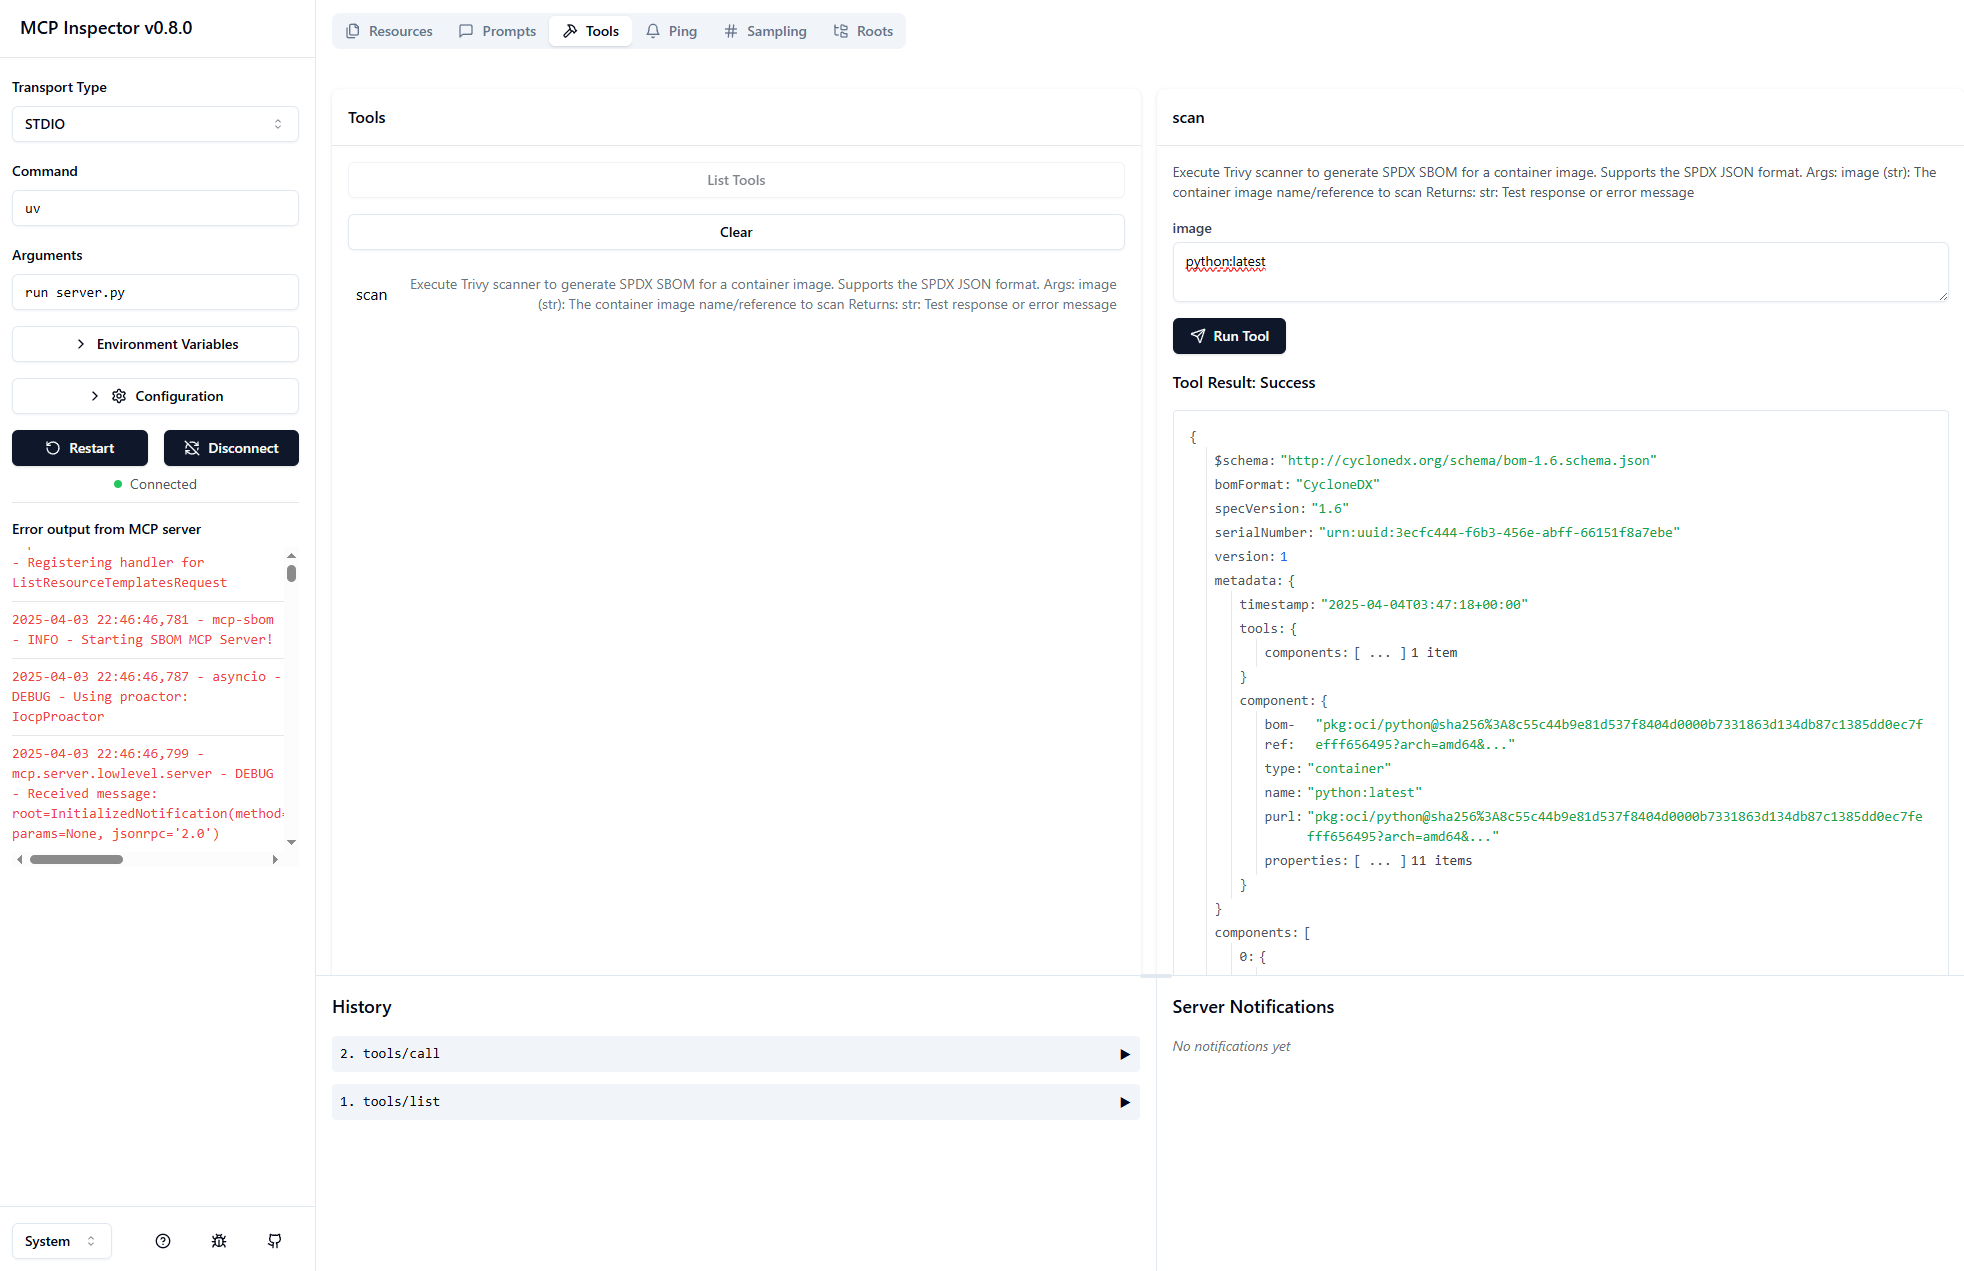
When running on Windows, use paths of the style:
C:/Users/gkh/src/mcp-sbom-server/src/mcp_sbomExecute Trivy scanner to generate SPDX SBOM for a container image.
Supports the SPDX JSON format.
Args:
image (str): The container image name/reference to scan
Returns:
str: Test response or error message
Inputs: image (required).
Recent tool additions, removals, and schema changes observed during successful MCP inspections.
Loading tool schema changelog…
Scored across 1 tool
With only one tool, there is no possibility of confusion or overlap between tools. The single 'scan' tool has a clearly defined purpose of generating SPDX SBOMs for container images using Trivy scanner.
With a single tool, naming consistency is inherently perfect. The tool name 'scan' follows a clear verb-based naming pattern that accurately describes its function without any conflicting naming conventions to compare against.
A single tool for an SBOM server feels insufficient for the apparent domain scope. While scanning is a core function, SBOM management typically involves additional operations like listing, retrieving, comparing, or validating SBOMs. The server appears to have significant functional gaps beyond the basic scan capability.
The tool surface is severely incomplete for an SBOM server. While scanning is essential, there are obvious gaps in the lifecycle: no tools for retrieving stored SBOMs, comparing different SBOM versions, validating SBOM formats, or managing SBOM metadata. This limited surface will likely cause agent failures when trying to perform comprehensive SBOM workflows.
A Model Context Protocol server for Wix AI tools
Model Context Protocol server for the Apideck Unified API. Connect any MCP-compatible agent framework to 100+ accounting systems, HRIS platforms, file storage providers, and more through one integration. More information https://www.apideck.com/mcp-server
Scans remote MCP servers for protocol, security, and TLS issues; exposes scan tools via MCP.
Security scanner for MCP servers. Detect vulnerabilities, prompt injection, and tool poisoning.