arch-mcp
The Arch Linux MCP server enables AI assistants to safely access and interact with the Arch Linux ecosystem including the Arch Wiki, AUR packages, and official repositories.
Search & Information Retrieval: Query Arch Wiki documentation and AUR packages with smart ranking by relevance, votes, popularity, or modification date
Secure Package Management: Install packages with comprehensive security checks, prioritizing official repositories and automatically auditing AUR packages before installation
System Maintenance: Perform safe, read-only checks for available system updates on Arch Linux systems
Security Analysis: Analyze PKGBUILD files for malicious commands, dangerous patterns, and suspicious network activity, plus evaluate package trustworthiness based on metadata
Direct URI Access: Retrieve specific resources using custom URI schemes (
archwiki://,aur://,archrepo://) for Wiki pages, PKGBUILDs, and package detailsGuided Workflows: Execute pre-built prompts for troubleshooting, dependency analysis, and pre-installation safety audits
Cross-Platform Support: Works on both Arch and non-Arch systems (with some Arch-specific features requiring Arch Linux)
Provides comprehensive access to the Arch Linux ecosystem including searching and accessing Arch Wiki documentation, browsing AUR packages with security analysis, querying official repositories, managing system packages, and performing security audits of PKGBUILDs and package metadata.
Click on "Deploy Server".
Wait a few minutes for the server to deploy. Once ready, it will show a "Started" state.
In the chat, type
@followed by the MCP server name and your instructions, e.g., "@arch-mcpsearch AUR for a terminal emulator"
That's it! The server will respond to your query, and you can continue using it as needed.
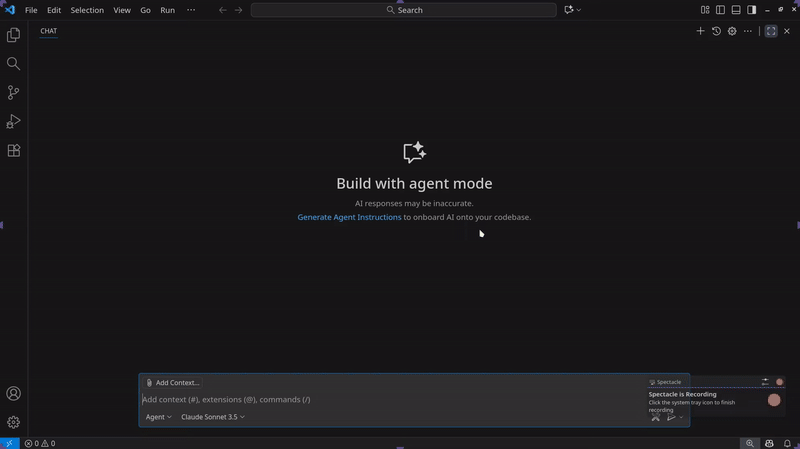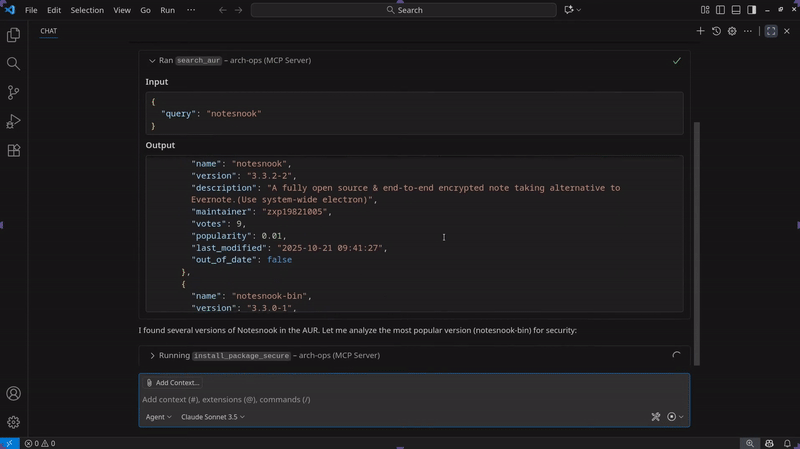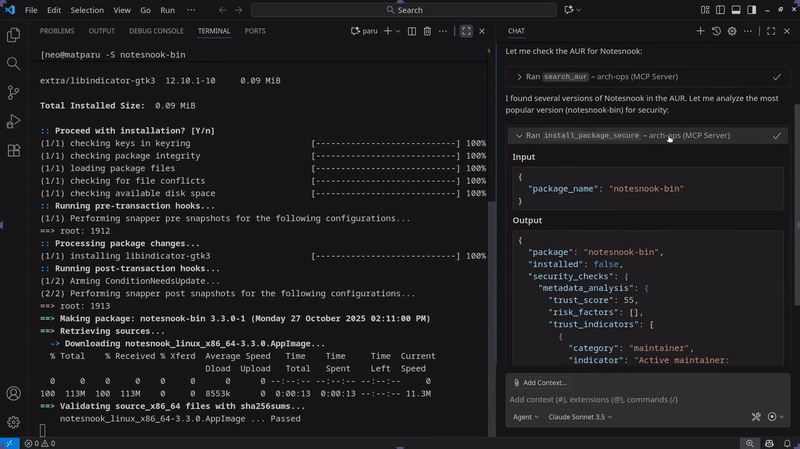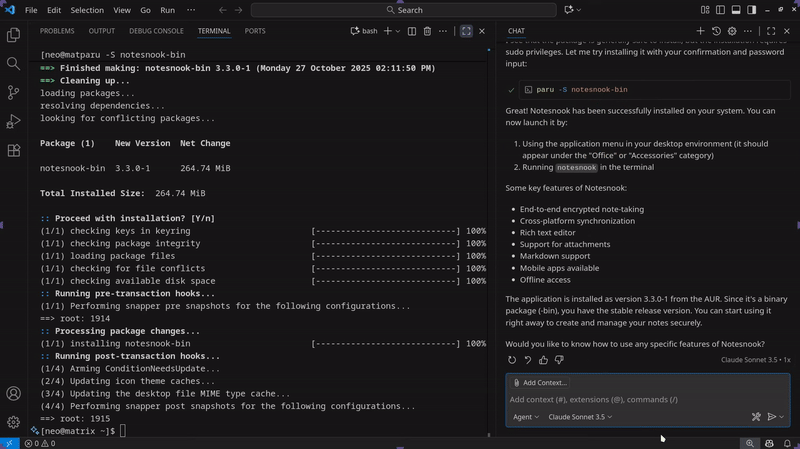
Here is a step-by-step guide with screenshots.
Arch Linux MCP Server
Disclaimer: Unofficial community project, not affiliated with Arch Linux.
A Model Context Protocol (MCP) server that bridges AI assistants with the Arch Linux ecosystem. Enables intelligent, safe, and efficient access to the Arch Wiki, AUR, and official repositories for AI-assisted Arch Linux usage on Arch and non-Arch systems.
Leverage AI to get digestible, structured results that are ready for follow up questions and actions.
📖 Complete Documentation with Comfy Guides
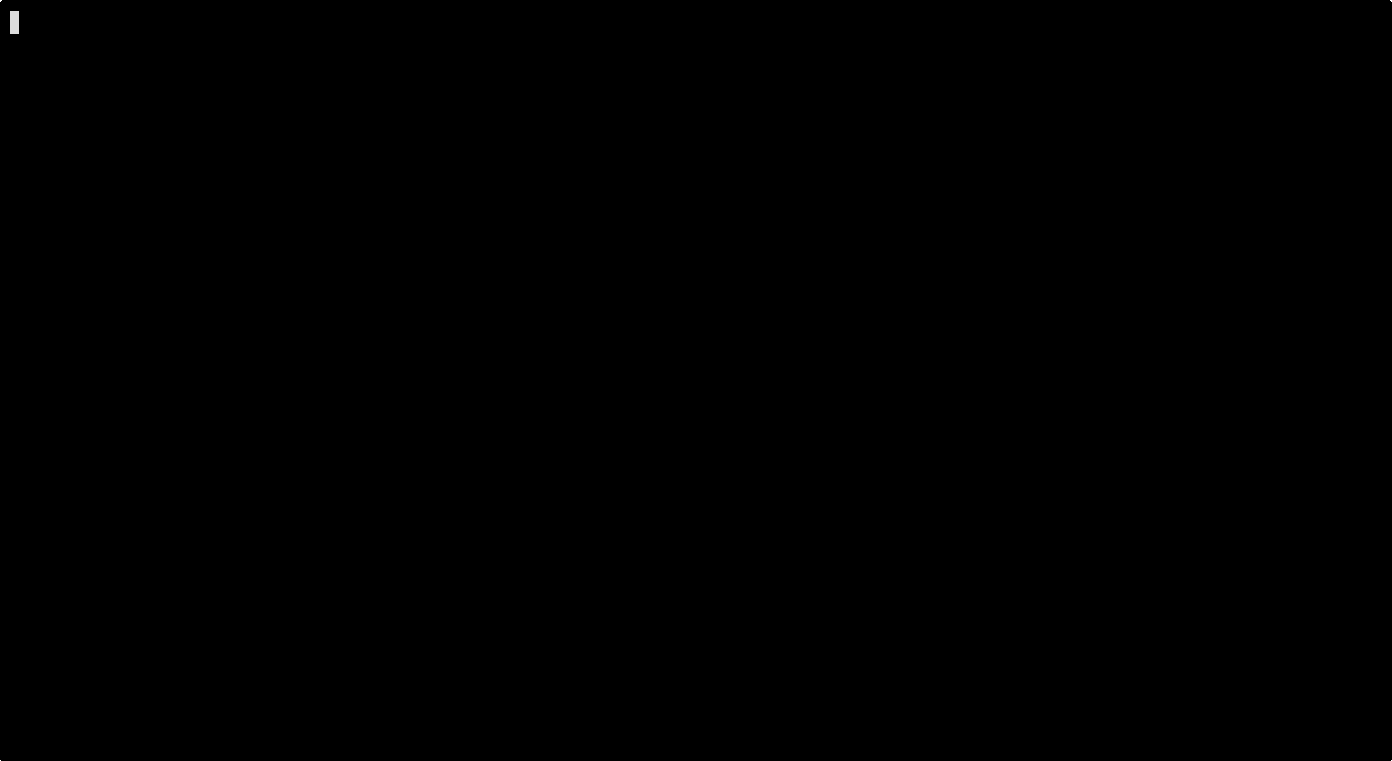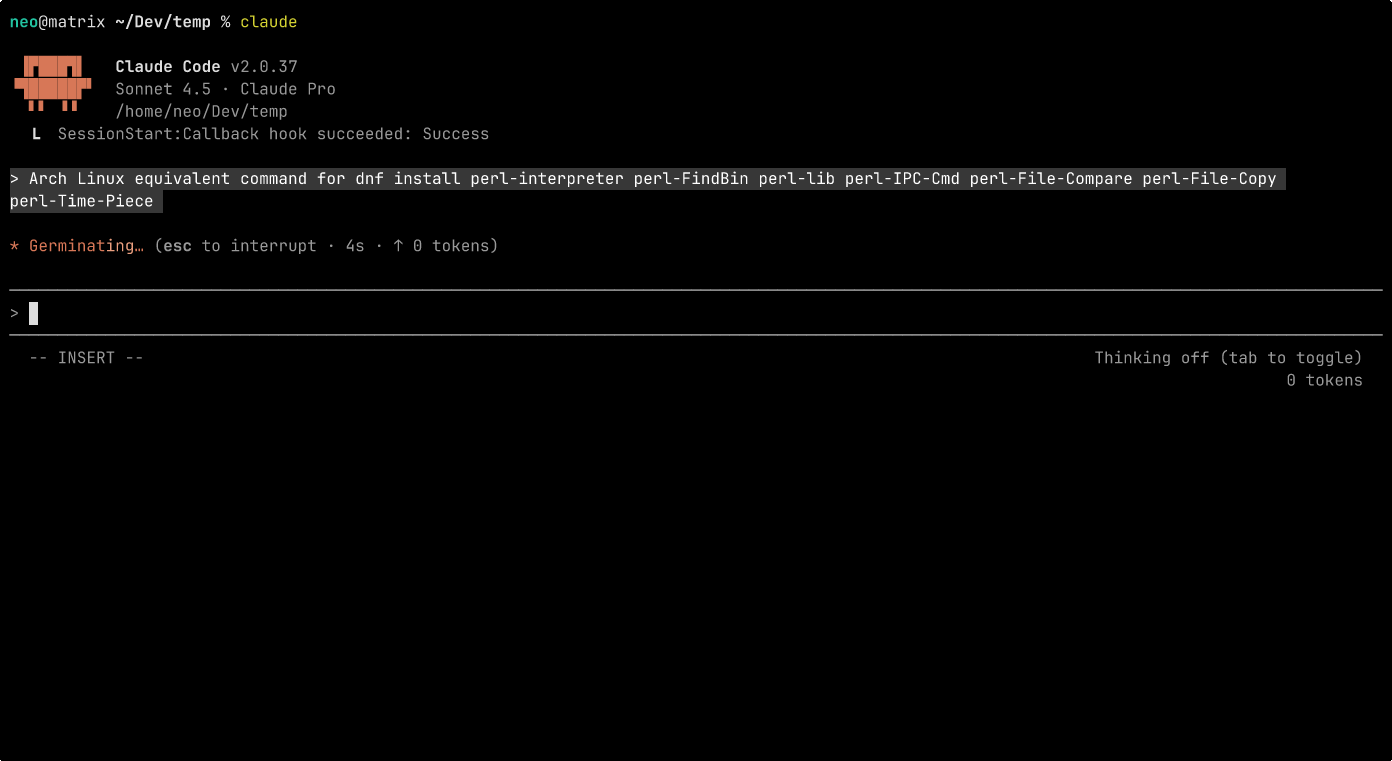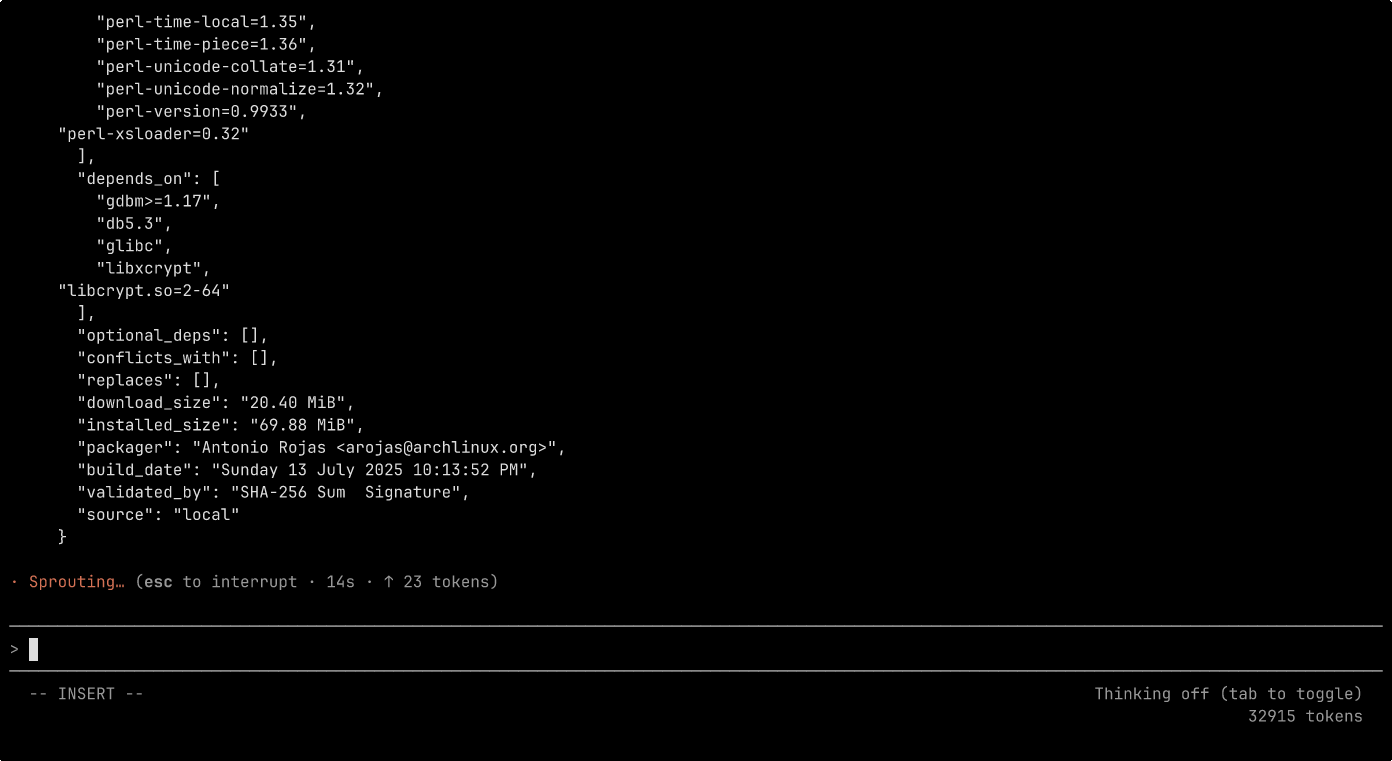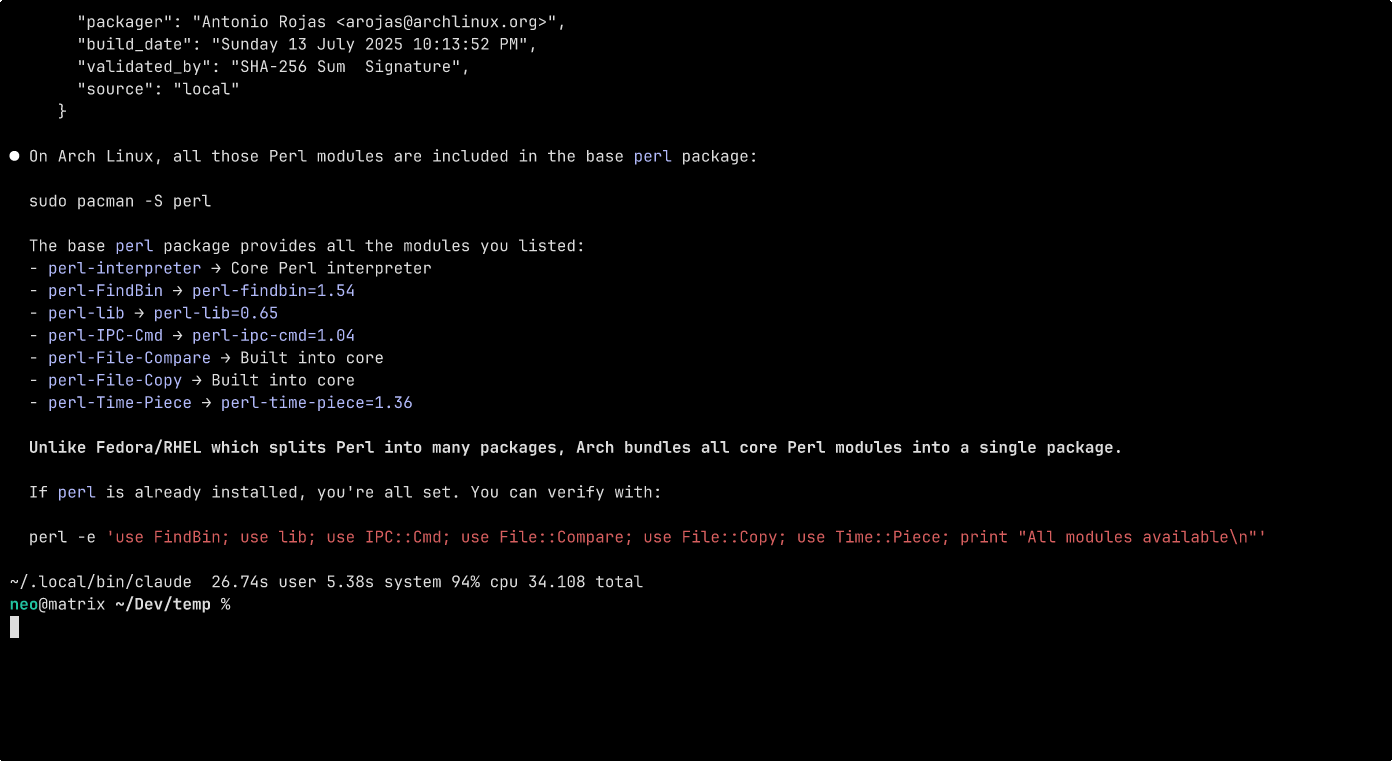
Sneak Peak into what's available
Resources (URI-based Access)
Direct access to Arch ecosystem data via custom URI schemes:
Documentation & Search
URI Scheme | Example | Returns |
|
| Markdown-formatted Wiki page |
Package Information
URI Scheme | Example | Returns |
|
| Official repository package details |
|
| AUR package metadata (votes, maintainer, dates) |
|
| Raw PKGBUILD with safety analysis |
System Packages (Arch only)
URI Scheme | Example | Returns |
|
| System installed packages list |
|
| Orphaned packages |
|
| Explicitly installed packages |
|
| All package groups |
|
| Packages in specific group |
|
| Package database sync status |
System Monitoring & Logs
URI Scheme | Example | Returns |
|
| System information (kernel, memory, uptime) |
|
| Disk space usage statistics |
|
| Failed systemd services |
|
| Recent boot logs |
|
| Recent package transactions |
|
| Failed package transactions |
News & Updates
URI Scheme | Example | Returns |
|
| Latest Arch Linux news |
|
| Critical news requiring manual intervention |
|
| News since last system update |
Configuration
URI Scheme | Example | Returns |
|
| Parsed pacman.conf configuration |
|
| Parsed makepkg.conf configuration |
|
| Currently configured mirrors |
|
| Mirror configuration health status |
Tools (Executable Functions)
Package Search & Information
Tool | Description | Platform |
| Query Arch Wiki with ranked results | Any |
| Search AUR (relevance/votes/popularity/modified) | Any |
| Get official package details (hybrid local/remote) | Any |
Package Lifecycle Management
Tool | Description | Platform |
| Check for available updates | Arch only |
| Install with security checks (blocks malicious packages) | Arch only |
| Remove packages - accepts single package name or list (with deps, forced) | Arch only |
Package Analysis & Maintenance
Tool | Description | Platform |
| Manage orphaned packages (2 actions: list orphaned packages, remove orphans). Always runs in dry-run mode first for safety. | Arch only |
| Check file integrity (modified/missing files) | Arch only |
| Manage install reasons (3 actions: list explicit packages, mark as explicit/dependency) | Arch only |
Package Organization
Tool | Description | Platform |
| Unified file-package ownership queries (3 modes: file→package, package→files, filename search) | Arch only |
| List all groups (base, base-devel, etc.) | Arch only |
| Show packages in specific group | Arch only |
System Monitoring & Diagnostics
Tool | Description | Platform |
| System info (kernel, memory, uptime) | Any |
| Disk usage with warnings | Any |
| Package cache size and age | Arch only |
| Find failed systemd services | systemd |
| Retrieve journalctl boot logs | systemd |
| Check package database sync status | Arch only |
Transaction History & Logs
Tool | Description | Platform |
| Unified tool for querying package history from pacman logs (4 query types). Examples: | Arch only |
News & Safety Checks
Tool | Description | Platform |
| Fetch Arch Linux news from RSS | Any |
| Find critical news (manual intervention required) | Any |
| News posted since last system update | Arch only |
Mirror Management
Tool | Description | Platform |
| Smart mirror management (4 actions: status, test, suggest, health). Examples: | Arch/Any |
Configuration Management
Tool | Description | Platform |
| Parse pacman.conf settings with optional focus. Examples: | Arch only |
| Parse makepkg.conf settings (CFLAGS, MAKEFLAGS, build configuration) | Arch only |
Security Analysis
Tool | Description | Platform |
| Comprehensive PKGBUILD analysis (50+ red flags) | Any |
| Package trust scoring (votes, maintainer, age) | Any |
Prompts (Guided Workflows)
Prompt | Purpose | Workflow |
| Diagnose system errors | Extract keywords → Search Wiki → Context-aware suggestions |
| Pre-installation safety audit | Fetch metadata → Analyze PKGBUILD → Security recommendations |
| Installation planning | Check repos → Map dependencies → Suggest install order |
| Safe update workflow | Check critical news → Verify disk space → List updates → Check services → Recommendations |
Related MCP server: Context7 MCP
Installation
Prerequisites
Python 3.11+
uv (recommended) or pip
Quick Install with uvx
uvx arch-ops-serverConfiguration
Claude / Cursor / Any MCP client that supports STDIO transport
{
"mcpServers": {
"arch-linux": {
"command": "uvx",
"args": ["arch-ops-server"]
}
}
}Opencode:
{
"$schema": "https://opencode.ai/config.json",
"mcp": {
"arch-linux": {
"type": "local",
"command": ["uvx", "arch-ops-server"]
}
}
}Contributing
Contributions are greatly appreciated. Please feel free to submit a pull request or open an issue and help make things better for everyone.
License
This project is dual-licensed under your choice of:
GPL-3.0-only - For those who prefer strong copyleft protections. See LICENSE-GPL
MIT License - For broader compatibility and adoption, including use in proprietary software and compatibility with platforms like Docker MCP Catalog. See LICENSE-MIT
You may use this software under the terms of either license. When redistributing or modifying this software, you may choose which license to apply.
By contributing to this project, you agree that your contributions will be licensed under both licenses.
Available Tools
22 toolsanalyze_makepkg_confARead-only
[CONFIG] Parse and analyze makepkg.conf. Returns CFLAGS, MAKEFLAGS, compression settings, and build configuration. Only works on Arch Linux. Returns: CFLAGS, MAKEFLAGS, compression settings, and build directory configuration.
| Name | Required | Description | Default |
|---|---|---|---|
No parameters | |||
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations declare readOnlyHint=true, and the description adds that it returns configuration details. No mention of potential errors or file requirements beyond Arch Linux. The description does not contradict annotations.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is short but contains redundant listing of return values twice ('Returns CFLAGS, MAKEFLAGS, compression settings, and build configuration'). This could be streamlined.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
For a zero-parameter, read-only config parser, the description adequately covers purpose, output, and platform constraint. It does not require an output schema since returns are enumerated.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
The tool has zero parameters, and the description does not need to add detail beyond the schema, which is already 100% covered. Baseline 4 applies as per guidelines.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it parses and analyzes makepkg.conf and lists specific returns (CFLAGS, MAKEFLAGS, etc.). It uniquely distinguishes from sibling tools like analyze_pacman_conf by focusing on the build configuration file.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
It explicitly notes 'Only works on Arch Linux', which is a key constraint. However, it does not provide guidance on when to use this tool over similar siblings (e.g., analyze_pacman_conf) nor when not to use it.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
analyze_pacman_confARead-only
[CONFIG] Parse and analyze pacman.conf with optional focus. Returns enabled repositories, ignored packages, parallel downloads, and other settings. Only works on Arch Linux. Examples: focus='full' (default) returns all settings; focus='ignored_packages' returns only ignored packages with warnings for critical ones; focus='parallel_downloads' returns only parallel downloads setting with optimization recommendations.
| Name | Required | Description | Default |
|---|---|---|---|
| focus | No | What to analyze: 'full' (all settings), 'ignored_packages' (only ignored packages), 'parallel_downloads' (only parallel downloads setting) | full |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations indicate readOnlyHint=true, and the description adds behavioral details: returns specific settings (repositories, ignored packages, parallel downloads), platform constraint (only Arch Linux), and examples of focus modes. This goes beyond the annotation's read-only indication.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is concise, starting with a clear tag and purpose, then succinctly covering returns, platform, and examples without unnecessary words. Every sentence adds value.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
The tool has a simple interface with one optional parameter and no output schema. The description covers the operation, parameter semantics, constraints, and examples, making it fully complete for an agent to use correctly.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100% with enum descriptions, but the description adds rich semantics for each focus value: 'full' returns all settings, 'ignored_packages' returns warnings for critical ones, 'parallel_downloads' returns optimization recommendations. This significantly aids correct parameter selection.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
Description explicitly states the verb 'Parse and analyze' and the resource 'pacman.conf' with optional focus parameter. The tool's purpose is clear and distinguishes itself from siblings like 'analyze_makepkg_conf' by name and resource.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description implies usage for analyzing pacman.conf on Arch Linux, but does not provide explicit guidance on when to use this tool over siblings like 'analyze_makepkg_conf' or 'diagnose_system'. No when-not-to-use or alternative recommendations.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
analyze_storageARead-only
[MONITORING] Unified storage analysis tool. Actions: disk_usage (check disk space for critical paths), cache_stats (analyze pacman package cache). Works on any system for disk_usage, Arch only for cache_stats.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Analysis type to perform |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already declare readOnlyHint=true. The description reinforces this with '[MONITORING]' and describes the actions as checks and analyses. It adds platform-specific behavior for cache_stats, which is beyond annotations. No mention of potential permissions (e.g., sudo) but adequate given read-only nature.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
Two sentences: first states overall purpose and lists actions, second specifies platform constraints. No wasted words, front-loaded with key information. Efficient and clear.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Despite no output schema, the description covers all necessary context: tool category, available actions, and platform-specific usage. For a simple tool with one parameter and no nested objects, the description is sufficient for an AI agent to select and invoke correctly.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema has one required parameter 'action' with enum values and description. The description enriches each enum value with behavior: 'disk_usage (check disk space for critical paths)', 'cache_stats (analyze pacman package cache)'. This provides meaning beyond the schema's enum labels.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it is a monitoring tool for storage analysis, listing two specific actions ('disk_usage', 'cache_stats') with brief descriptions. It distinguishes from sibling tools by prefixing '[MONITORING]' and specifying platform constraints.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description provides per-action platform constraints: 'Works on any system for disk_usage, Arch only for cache_stats.' It gives clear guidance on when each action is applicable, but does not explicitly differentiate from sibling tools like 'analyze_makepkg_conf' or 'diagnose_system'.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
audit_package_securityBRead-only
[SECURITY] Comprehensive security audit for AUR packages. Actions: pkgbuild_analysis (scan PKGBUILD for 50+ red flags), metadata_risk (evaluate trustworthiness via votes/maintainer/age). Examples: audit_package_security(action='pkgbuild_analysis', pkgbuild_content='...'), audit_package_security(action='metadata_risk', package_name='yay'). ⚠️ Always audit AUR packages before installing.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Type of security audit | |
| pkgbuild_content | No | PKGBUILD content for analysis | |
| package_name | No | Package name for metadata analysis | |
| package_info | No | Pre-fetched package metadata |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
The annotations already declare readOnlyHint=true, so the description's 'security audit' label is consistent. The description adds details about what each action does (e.g., scanning for red flags, evaluating trustworthiness). However, it does not disclose whether network calls are needed for metadata analysis or other runtime behaviors. It is adequate but not comprehensive.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is concise, starting with a clear heading and bullet points for actions. It includes examples and a warning. Every sentence adds value. It is well-structured and not overly verbose.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given the absence of an output schema, the description should indicate what the tool returns (e.g., a report, JSON, or list of issues). It does not. The tool has four parameters, including a nested object, but the description does not explain the return format or provide guidance on using the package_info parameter. The overall context is incomplete for a comprehensive audit tool.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
The input schema covers all parameters with descriptions. The description adds significant context beyond the schema: 'scan PKGBUILD for 50+ red flags' for pkgbuild_analysis and 'evaluate trustworthiness via votes/maintainer/age' for metadata_risk. Examples also clarify parameter usage. This goes beyond the schema's minimal descriptions.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it performs security audits for AUR packages with two specific actions (pkgbuild_analysis and metadata_risk). Examples further clarify usage. It distinguishes from siblings like verify_package_integrity by focusing on AUR. However, it could be more explicit about differentiating from other analysis tools.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description implies usage before installing AUR packages with '⚠️ Always audit AUR packages before installing.' It provides examples for each action but does not explicitly state when not to use or mention alternatives like verify_package_integrity for official packages. The guidance is implied rather than explicit.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
check_database_freshnessARead-only
[MAINTENANCE] Check when package databases were last synchronized. Warns if databases are stale (> 24 hours). Only works on Arch Linux. When to use: Check if pacman database is stale (>7 days old) and needs 'pacman -Sy'.
| Name | Required | Description | Default |
|---|---|---|---|
No parameters | |||
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations declare readOnlyHint=true, confirming safe read-only operation. Description adds that it warns on staleness, which goes beyond annotations. The inconsistent threshold (24h vs 7d) is a minor flaw, but overall behavioral context is adequate.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
Description is short and to the point, with a separate 'When to use' line. The inconsistency in staleness thresholds is a minor distraction, but overall it is efficient and well-structured.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Missing output schema means return format is unspecified (only 'warns' is mentioned). The inconsistent threshold (24h vs 7d) creates uncertainty. While the tool's purpose is clear, the description is not fully complete for an agent to invoke correctly without additional knowledge.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Input schema has zero parameters with 100% coverage; description adds no parameter detail, which is acceptable. With no parameters, the description doesn't need to compensate, so a score of 4 is appropriate.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states the tool checks when package databases were last synchronized and warns if stale. It specifies it only works on Arch Linux, distinguishing it from generic tools. However, internal inconsistency between '>24 hours' and '>7 days' reduces clarity slightly.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
Provides explicit guidance: 'When to use: Check if pacman database is stale (>7 days old) and needs pacman -Sy.' It also marks the tool as maintenance-related and restricts to Arch Linux. Does not explicitly list when not to use or alternatives, but the context is clear.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
check_updates_dry_runARead-only
[LIFECYCLE] Check for available system updates without applying them. Only works on Arch Linux systems. Requires pacman-contrib package. Safe read-only operation that shows pending updates. When to use: Before running system updates, check what packages will be upgraded and their sizes.
| Name | Required | Description | Default |
|---|---|---|---|
No parameters | |||
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already declare readOnlyHint=true, and the description adds 'Safe read-only operation' to reinforce this. It also includes lifecycle indicator [LIFECYCLE] and system requirements, providing additional behavioral context beyond annotations.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is concise with three sentences, each adding value: purpose, system requirements, and usage guidance. It is front-loaded with the lifecycle tag and contains no wasted words.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Despite no output schema, the description explains what the tool shows (pending updates with package sizes). For a no-parameter tool on a specific system, it provides sufficient completeness for an agent to use correctly.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
There are no parameters, so the baseline is 4. The description does not need to add parameter information, and it appropriately focuses on the tool's purpose.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it checks for available system updates without applying them. Verb 'check' and resource 'system updates' are specific, and the 'dry run' concept distinguishes it from sibling tools like install_package_secure or remove_packages.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
It explicitly says 'Before running system updates, check what packages will be upgraded and their sizes,' providing a clear when-to-use context. It also specifies it only works on Arch Linux and requires pacman-contrib. While it doesn't mention when not to use or alternatives, the context is sufficient.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
diagnose_systemARead-only
[MONITORING] Unified system diagnostics for systemd-based systems. Actions: failed_services (check for failed systemd services), boot_logs (retrieve recent boot logs). Works on systemd-based systems only.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Diagnostic action to perform | |
| lines | No | Number of log lines (for boot_logs). Default: 100 |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
The readOnlyHint annotation already marks this as a safe read operation. Beyond that, the description adds meaningful behavioral context: it lists the two diagnostic actions and explicitly states the systemd-only limitation. This helps the agent understand what the tool checks (failed services) and retrieves (boot logs), and under what conditions it applies. No contradictions with annotations.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is a single, compact sentence with a clear [MONITORING] tag upfront. It packs the core purpose, the available actions, and the systemd constraint into a minimal number of words without redundancy. Every part earns its place, making it easy to parse and act upon.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
For a tool with low complexity (one required enum param, one optional param, no output schema), the description is sufficient to understand what it does and under what constraints. The absence of an output schema means return values are not explicitly described, but the actions are simple enough that an agent can infer the likely diagnostic output. Slight deductions for not mentioning any error conditions or prerequisites beyond systemd.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
The schema already covers both parameters (action, lines) with 100% coverage, so the baseline is 3. However, the description adds semantic meaning to the action enum values by explaining what each action does ('check for failed systemd services' and 'retrieve recent boot logs'), which is not present in the schema's generic description. This elevates the score above baseline.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states the tool's purpose: 'Unified system diagnostics for systemd-based systems' and enumerates the two specific actions (failed_services and boot_logs) with brief explanations. This distinguishes it as a diagnostic tool focused on systemd systems, setting it apart from siblings like get_system_info or run_system_health_check.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description gives a clear environment constraint ('Works on systemd-based systems only') which implies when the tool is appropriate, but it does not explicitly mention alternatives or when not to use it. For example, it doesn't say 'for non-systemd systems, use X' or compare with run_system_health_check. Thus, usage guidance is implied rather than explicit.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
fetch_newsARead-only
[DISCOVERY] Unified news fetching from Arch Linux. Actions: latest (get recent news), critical (find news requiring manual intervention), since_update (news since last system update). Works on any system for latest/critical, Arch only for since_update.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Type of news query | |
| limit | No | Maximum news items (for latest/critical). Default: 10 | |
| since_date | No | ISO date to filter from (for latest action) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
The readOnlyHint annotation already indicates a read-only operation. The description adds the cross-platform vs Arch-only constraint, which is valuable behavioral context beyond annotations. However, it omits details such as return format, pagination, or error behavior. With annotations covering safety, a 3 is appropriate.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is a single concise paragraph, front-loaded with '[DISCOVERY]' and a clear summary. Every sentence adds value: tool purpose, action list, and platform constraints. No wasted words or redundancy.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given the moderate complexity (three actions, platform dependencies), the description covers the key behavioral differences and input parameters. No output schema exists, but for a fetch tool this is acceptable. It could briefly mention ordering or error handling for a perfect score, but current level is sufficient.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Input schema coverage is 100%, and the schema already describes each parameter (action enum, limit with default, since_date format). The description reinforces the action meanings and adds cross-platform info, but does not provide new details beyond the schema. Baseline 3 is correct as the schema does the heavy lifting.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description explicitly states 'Unified news fetching from Arch Linux' and enumerates three actions (latest, critical, since_update), providing a specific verb ('fetch') and resource ('news'). This clearly distinguishes it from all sibling tools, which are focused on other aspects like configuration analysis or package management.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description gives clear context for when to use each action: 'Works on any system for latest/critical, Arch only for since_update.' This informs the agent about platform dependencies. While it does not explicitly list alternatives, the sibling tools are unrelated to news fetching, so no exclusion is needed.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
get_official_package_infoARead-only
[DISCOVERY] Get information about an official Arch repository package (Core, Extra, etc.). Uses local pacman if available, otherwise queries archlinux.org API. Always prefer official packages over AUR when available. Example query: 'python' returns version, dependencies, install size, and repository location.
| Name | Required | Description | Default |
|---|---|---|---|
| package_name | Yes | Exact package name |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Beyond the readOnlyHint annotation, the description discloses the execution method (local pacman vs. API) and return fields (version, dependencies, install size, repository location). This context helps the agent understand side effects and output, though error handling is missing.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is single paragraph, front-loaded with purpose, followed by mechanism, preference rule, and example. Every sentence adds value, though it could be structured with bullet points for even quicker scanning.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given no output schema, the description covers return fields and behavior (local vs. API). It addresses the parameter and usage context. Missing error cases, but the simple 1-parameter tool is adequately documented for most use cases.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
The input schema fully describes the parameter (exact package name), but the description adds an example ('python'), illustrating usage and reinforcing the exact match requirement. This adds value beyond the schema alone.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states the tool retrieves information about official Arch repository packages, differentiating it from AUR tools like search_aur. The verb 'Get' and resource 'official package info' are specific, and the preference rule further disambiguates from siblings.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description provides clear guidance: prefer official packages over AUR, and it explains the local/API fallback. However, it does not explicitly name alternative tools or specify when not to use this tool, leaving some room for improvement.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
get_system_infoARead-only
[MONITORING] Get comprehensive system information including kernel version, architecture, hostname, uptime, and memory statistics. Works on any system. Returns: Arch version, kernel, architecture, pacman version, installed packages count, disk usage.
| Name | Required | Description | Default |
|---|---|---|---|
No parameters | |||
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
The description adds value beyond the readOnlyHint annotation by listing specific return fields (Arch version, kernel, etc.), but does not disclose any potential performance impact, permission requirements, or other behavioral traits. The annotation already covers safety, so the description provides moderate additional context.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is very concise, using a clear structure with a [MONITORING] tag, a sentence about what it does, and a list of returns. Every sentence is informative and there is no fluff.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given no parameters and no output schema, the description adequately documents the return values and scope (system info). It is complete for the tool's simplicity and the annotations (readOnlyHint) are consistent.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
No parameters exist, and schema coverage is 100% (since there are none). The description does not need to add parameter information. Baseline 4 is appropriate for a parameterless tool.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it gets comprehensive system info and lists specific items (kernel, architecture, etc.). However, it does not explicitly differentiate itself from sibling tools like analyze_storage or run_system_health_check, so it loses a point for lack of distinctiveness.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description only says 'Works on any system,' which implies a condition but provides no guidance on when to use this tool versus alternatives. There is no mention of when not to use it or what scenarios favor other sibling tools.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
install_package_secureADestructive
[LIFECYCLE] Install a package with comprehensive security checks. Workflow: 1. Check official repos first (safer) 2. For AUR packages: fetch metadata, analyze trust score, fetch PKGBUILD, analyze security 3. Block installation if critical security issues found 4. Check for AUR helper (paru > yay) 5. Install with --noconfirm if all checks pass. Only works on Arch Linux. Requires sudo access and paru/yay for AUR packages.
| Name | Required | Description | Default |
|---|---|---|---|
| package_name | Yes | Name of package to install (checks official repos first, then AUR) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations include destructiveHint: true, and the description expands with security workflow details, blocking conditions, and dependency on helpers. It does not cover failure handling or rollback, but adds value beyond annotations.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is detailed with numbered steps but could be more concise. Important context (Arch Linux, sudo) appears late. Front-loading key prerequisites would improve structure.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
The description covers lifecycle, prerequisites, and workflow steps. Missing details on error handling, output format, or success indicators, but the single-param nature and destructiveHint reduce the need for extensive context.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Only one parameter (package_name) with 100% schema coverage. The description adds no extra meaning beyond the schema's description. Baseline score of 3 is appropriate.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states the tool installs a package with comprehensive security checks, using a specific workflow. It distinguishes from sibling tools like remove_packages or check_updates_dry_run by specifying the security lifecycle and Arch Linux context.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description explicitly states prerequisites (Arch Linux, sudo, paru/yay) and the install workflow. It implies when to use this tool (for secure installation) but does not explicitly define when not to use it or suggest alternatives like search_aur for information-only needs.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
manage_groupsARead-only
[ORGANIZATION] Unified group management tool. Actions: list_groups (all groups), list_packages_in_group (packages in specific group). Examples: manage_groups(action='list_groups'), manage_groups(action='list_packages_in_group', group_name='base-devel')
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Operation to perform | |
| group_name | No | Group name (required for list_packages_in_group) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already declare readOnlyHint=true, indicating this is a read-only operation. The description reinforces this by describing listing actions. It adds no additional behavioral details beyond what annotations and schema provide, such as side effects or error states.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is extremely concise, consisting of two sentences plus examples. It front-loads the purpose and directly lists actions. No redundant or unnecessary information.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
For a simple tool with two read-only actions and no output schema, the description fully covers the functionality. It explains both actions and their parameter requirements. Sibling tools are diverse but this tool's scope is narrow and well-covered.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, so parameters are fully described in the input schema. The description adds value by providing example parameter values and showing the required combination (group_name for list_packages_in_group), but this is a minor addition over the schema's own descriptions.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it is a unified group management tool and explicitly lists the two supported actions (list_groups and list_packages_in_group) with examples. It distinguishes itself from sibling tools by focusing specifically on group operations.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description provides clear context for using each action (list all groups vs. list packages in a specific group) with concrete examples. It does not explicitly mention when not to use this tool or compare directly with alternatives, but the usage is well-implied.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
manage_install_reasonA
[MAINTENANCE] Unified tool for managing package install reasons. Supports three actions: 'list' (list all explicitly installed packages), 'mark_explicit' (prevent package from being removed as orphan), and 'mark_dependency' (allow package to be auto-removed with orphans). Only works on Arch Linux. Examples: action='list' → returns all user-installed packages; action='mark_explicit', package_name='python-pip' → keeps package even when dependencies change; action='mark_dependency', package_name='lib32-gcc-libs' → allows auto-removal with orphans.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Action to perform: 'list' (list explicit packages), 'mark_explicit' (mark as user-installed), or 'mark_dependency' (mark as auto-removable) | |
| package_name | No | Package name (required for mark_explicit and mark_dependency actions) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations indicate readOnlyHint=false and destructiveHint=false, so the tool may write but is not destructive. The description adds behavioral context: it only works on Arch Linux, and the three actions have different write implications. No contradictions with annotations.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is relatively concise and well-structured, starting with a [MAINTENANCE] tag and listing actions and examples. It could be slightly trimmed without losing value, but it earns its length.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given the tool's moderate complexity and no output schema, the description covers the main actions and their effects. It explains the return for 'list' but not for 'mark_*' actions; however, those likely return success/failure, which is implied.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, so the schema already documents parameters well. The description adds examples that clarify when package_name is required, but does not provide additional parameter semantics beyond what the schema and enums convey.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description uses a clear verb 'managing install reasons' and specifies three distinct actions ('list', 'mark_explicit', 'mark_dependency') with precise outcomes. It clearly distinguishes this tool from siblings like 'manage_orphans' by focusing on install reason management.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description provides explicit use cases for each action and gives multiple examples. While it doesn't explicitly state when not to use the tool or name alternatives, the context and examples are clear enough for correct selection.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
manage_orphansA
[MAINTENANCE] Unified tool for managing orphaned packages (dependencies no longer required). Supports two actions: 'list' (show orphaned packages) and 'remove' (remove orphaned packages). Only works on Arch Linux. Requires sudo access for removal. Examples: action='list' → shows all orphaned packages with disk usage; action='remove', dry_run=true → preview what would be removed; action='remove', dry_run=false, exclude=['pkg1'] → remove all orphans except 'pkg1'.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Action to perform: 'list' (list orphaned packages) or 'remove' (remove orphaned packages) | |
| dry_run | No | Preview what would be removed without actually removing (only for remove action). Default: true | |
| exclude | No | List of package names to exclude from removal (only for remove action) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
The description discloses key behavioral traits beyond annotations: requires sudo, only works on Arch, dry_run functionality, and removal behavior. However, the destructiveHint=false annotation contradicts the description's mention of package removal, which is destructive. This is a minor issue given the description's clarity.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is well-structured with a clear topic, actions listed first, then requirements, then examples. Every sentence serves a purpose, and the use of examples enhances understanding without redundancy.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
While the description covers platform, permissions, and action details, it lacks precise information about the output format for the 'list' action (e.g., whether it's a list of package names or includes size). Without an output schema, more detail on return values would improve completeness.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, but the description adds significant value by explaining default behavior (dry_run=true), providing examples for each action, and clarifying the effect of the exclude parameter. This goes beyond the schema's basic type and enum definitions.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states the tool is for managing orphaned packages with two actions (list and remove), using specific verbs and resource. It distinguishes itself from sibling tools like remove_packages by focusing exclusively on orphaned packages.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description provides explicit usage context: works only on Arch Linux, requires sudo for removal, and includes examples for different scenarios. It does not explicitly state when not to use or alternatives, but the specificity to orphans makes usage clear.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
optimize_mirrorsARead-only
[MIRRORS] Smart mirror management - consolidates 4 mirror operations. Actions: 'status' (list configured mirrors), 'test' (test mirror speeds), 'suggest' (get optimal mirrors from archlinux.org), 'health' (full health check). Examples: optimize_mirrors(action='status', auto_test=True) lists and tests all mirrors; optimize_mirrors(action='suggest', country='US', limit=5) suggests top 5 US mirrors; optimize_mirrors(action='health') checks for issues and gives recommendations.
| Name | Required | Description | Default |
|---|---|---|---|
| action | Yes | Operation to perform: 'status' (list mirrors), 'test' (test speeds), 'suggest' (get recommendations), 'health' (full check) | |
| country | No | Optional country code for suggestions (e.g., 'US', 'DE') - action='suggest' only | |
| mirror_url | No | Specific mirror URL to test - action='test' only | |
| limit | No | Number of mirrors for suggestions (default 10) | |
| auto_test | No | If true, test mirrors after listing - action='status' only |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations indicate readOnlyHint=true, and the description aligns with this by describing read-only operations like listing, testing, and suggesting. It adds behavioral context such as what each action does (e.g., health check gives recommendations).
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is well-structured with a tag, action list, and examples. It is informative without being overly verbose, though the examples could be slightly more compact.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
While the description explains what each action does, it does not specify the return format or output structure. For a tool with no output schema, more detail on the response (e.g., list of mirrors, test results) would improve completeness.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, so baseline is 3. The description adds examples showing parameter combinations (e.g., action='suggest' with country and limit), but the schema already documents all parameters and their constraints.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it is for 'smart mirror management' and lists four specific actions (status, test, suggest, health). It distinguishes itself from sibling tools which focus on system configuration analysis and package management.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description provides clear context for each action with examples and notes which parameters apply to which action. However, it does not explicitly mention when not to use this tool or suggest alternatives among siblings.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
query_file_ownershipARead-only
[ORGANIZATION] Unified tool for querying file-package ownership relationships. Supports three modes: 'file_to_package' (find which package owns a file), 'package_to_files' (list all files in a package with optional filtering), and 'filename_search' (search for files across all packages). Only works on Arch Linux. Examples: mode='file_to_package', query='/usr/bin/python' → returns 'python' package; mode='package_to_files', query='systemd', filter_pattern='.service' → lists all systemd service files; mode='filename_search', query='.desktop' → finds all packages with desktop entries.
| Name | Required | Description | Default |
|---|---|---|---|
| query | Yes | Query string: file path for file_to_package mode, package name for package_to_files mode, or filename pattern for filename_search mode | |
| mode | Yes | Query mode: 'file_to_package' (find package owner), 'package_to_files' (list package files), or 'filename_search' (search across packages) | |
| filter_pattern | No | Optional regex pattern to filter files (only used in package_to_files mode, e.g., '*.conf' or '/etc/') |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already declare readOnlyHint=true, so the description mainly adds mode-specific behavior details but does not disclose additional behavioral traits beyond what annotations provide.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
Description is front-loaded with purpose and includes examples, but is slightly verbose; every sentence adds value.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given the complexity of three modes and no output schema, the description adequately covers usage with examples, but lacks return value details.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, description adds examples and clarifies filter_pattern usage only in package_to_files mode, but does not add significant new semantic meaning.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it is a unified tool for querying file-package ownership relationships with three distinct modes, distinguishing it from sibling tools that handle other package operations.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
Specifies that it only works on Arch Linux and provides examples for each mode, but does not explicitly compare with alternatives like query_package_history.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
query_package_historyARead-only
[HISTORY] Unified tool for querying package history from pacman logs. Supports four query types: 'all' (recent transactions), 'package' (specific package install/upgrade history), 'failures' (failed transactions), and 'sync' (database sync history). Only works on Arch Linux. Examples: query_type='all', limit=50 → recent transactions; query_type='package', package_name='docker' → when docker was installed; query_type='failures' → find errors; query_type='sync', limit=20 → sync history.
| Name | Required | Description | Default |
|---|---|---|---|
| query_type | Yes | Type of query: 'all' (recent transactions), 'package' (package history), 'failures' (failed transactions), or 'sync' (database sync history) | |
| package_name | No | Package name (required for query_type='package') | |
| limit | No | Maximum number of results to return (default 50) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already declare readOnlyHint=true. Description adds that it reads pacman logs and only works on Arch Linux. This provides useful behavioral context beyond annotations, though it does not detail resource usage or output format.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is a single, well-organized paragraph that front-loads the purpose, then lists query types with examples. Every sentence adds value with no redundancy.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Covers all four query types with examples, platform constraint, and required parameter. No output schema exists, but the description doesn't need to specify return format. It is adequately complete for a read-only query tool.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, but the description adds meaning with examples (e.g., 'when docker was installed' for package_name) and clarifies the conditional requirement for package_name. This goes beyond the schema's enum labels.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it queries package history from pacman logs, lists all four query types with examples, and is distinct from sibling tools that cover other aspects (e.g., install, update, analyze).
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
Provides explicit examples for each query type, implying when to use them (e.g., 'when docker was installed' for package query). States the platform restriction (Arch Linux). Does not explicitly compare to alternatives, but the examples serve as guidance.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
remove_packagesADestructive
[LIFECYCLE] Unified tool for removing packages (single or multiple). Accepts either a single package name or a list of packages. Supports removal with dependencies and forced removal. Only works on Arch Linux. Requires sudo access. Examples: packages='firefox', remove_dependencies=true → removes Firefox with its dependencies; packages=['pkg1', 'pkg2', 'pkg3'] → batch removal of multiple packages; packages='lib', force=true → force removal ignoring dependencies (dangerous!).
| Name | Required | Description | Default |
|---|---|---|---|
| packages | Yes | Package name (string) or list of package names (array) to remove | |
| remove_dependencies | No | Remove packages and their dependencies (pacman -Rs). Default: false | |
| force | No | Force removal ignoring dependencies (pacman -Rdd). Use with caution! Default: false |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already include destructiveHint=true, and the description adds value by detailing the need for sudo, the behavior of dependencies and force flags, and the dangers of forced removal. No contradictions.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
Description is reasonably concise given the detail needed; front-loaded with purpose and tag, then examples. Could trim some redundancy but overall efficient.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
No output schema, but the description sufficiently explains the tool's behavior for a removal operation. It covers input flexibility, dependency handling, and safety warnings.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema has 100% coverage, but the description adds concrete examples (e.g., 'packages='firefox', remove_dependencies=true → removes Firefox with its dependencies') and explains the pacman flags, which adds meaning beyond the schema.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
Description clearly states this is a tool for removing packages on Arch Linux, with specific verb 'remove' and resource 'packages'. It distinguishes itself from sibling tools like install_package_secure, manage_groups, etc., by focusing solely on removal.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
Provides explicit context: 'Only works on Arch Linux', 'Requires sudo access', and examples showing different usage patterns. Does not explicitly state when not to use, but the purpose is clear and no sibling tool does removal.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
run_system_health_checkARead-only
[MONITORING] Run a comprehensive system health check. Integrates multiple diagnostics to provide a complete overview of system status, including disk space, failed services, updates, orphan packages, and more. Only works on Arch Linux. Comprehensive check: Updates available, disk space, failed services, database freshness, orphans, and critical news.
| Name | Required | Description | Default |
|---|---|---|---|
No parameters | |||
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
The description adds context beyond the readOnlyHint annotation by listing the specific diagnostics included, but it does not disclose other behavioral traits such as potential performance impact or required permissions. The annotation already indicates no destructive side effects, so the description's added value is moderate.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is relatively concise with three sentences, front-loading the purpose. The last sentence repeats some content, but overall it is efficient and structured appropriately.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given no parameters or output schema, the description fully explains the tool's purpose, scope, and constraints. It covers all necessary context for a monitoring tool with read-only behavior.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
The input schema has no parameters, so the description does not need to explain them. The baseline for 0 parameters is 4, and the description is adequate.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states 'Run a comprehensive system health check' with a specific verb and resource. It distinguishes itself from sibling tools (e.g., analyze_storage, check_database_freshness) by being a combined diagnostic that integrates multiple checks.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description explicitly notes 'Only works on Arch Linux' and lists the checks it performs (disk space, failed services, updates, etc.), which helps the agent decide when to use this comprehensive tool versus more specific sibling tools. However, it does not explicitly mention when not to use it.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
search_archwikiARead-only
[DISCOVERY] Search the Arch Wiki for documentation. Returns a list of matching pages with titles, snippets, and URLs. Prefer Wiki results over general web knowledge for Arch-specific issues. Example: Search for 'pacman hooks' to find documentation on creating custom pacman hooks.
| Name | Required | Description | Default |
|---|---|---|---|
| query | Yes | Search query (keywords or phrase) | |
| limit | No | Maximum number of results (default: 10) |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already declare readOnlyHint=true, and the description adds that it 'Returns a list of matching pages with titles, snippets, and URLs', which provides additional behavioral details. However, it does not disclose any other behaviors or side effects.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
The description is extremely concise: two sentences plus an example. It is front-loaded with the purpose and every sentence contributes meaningfully. No wasted words.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
For a simple search tool with two parameters and no output schema, the description adequately covers the purpose, return format, and usage context. It could mention the default limit of 10, but that is already in the schema.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100% with descriptions for both parameters. The description adds value by including an example ('Search for pacman hooks'), which illustrates the query parameter's usage beyond the schema.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states 'Search the Arch Wiki for documentation' which is a specific verb and resource. It is distinguished from sibling tools like search_aur, and the purpose is unmistakable.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
The description advises to 'Prefer Wiki results over general web knowledge for Arch-specific issues', providing clear context for when to use this tool. It does not explicitly state when not to use, but the context is sufficient.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
search_aurARead-only
[DISCOVERY] Search the Arch User Repository (AUR) for packages with smart ranking. ⚠️ WARNING: AUR packages are user-produced and potentially unsafe. Returns package info including votes, maintainer, and last update. Always check official repos first using get_official_package_info. Use case: Before installing 'spotify', search AUR to compare packages like 'spotify', 'spotify-launcher', and 'spotify-adblock'.
| Name | Required | Description | Default |
|---|---|---|---|
| query | Yes | Package search query | |
| limit | No | Maximum number of results (default: 20) | |
| sort_by | No | Sort method: 'relevance' (default), 'votes', 'popularity', or 'modified' | relevance |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations already provide readOnlyHint, and the description adds a safety warning about user-produced packages and states the returned info (votes, maintainer, last update), enhancing transparency beyond annotations. No contradiction.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
Every sentence serves a purpose: purpose, warning, return info, guidance, example. No fluff, well-structured with a warning icon. Ideal length for quick comprehension.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
Given 3 parameters, no output schema, and readOnlyHint annotation, the description covers all essential aspects: what it does, what it returns, safety considerations, and usage patterns. It feels complete for a search tool.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema coverage is 100%, so baseline is 3. The description adds context by mentioning 'smart ranking' and the sort options, and clarifies the limit default and query behavior, providing value beyond the schema.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states the verb 'search' and the resource 'Arch User Repository', and it distinguishes from sibling tools like get_official_package_info and search_archwiki by specifying that it searches AUR with smart ranking.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
Explicitly instructs to check official repos first with get_official_package_info, warns about AUR package safety, and provides a concrete use case, making it clear when and how to use this tool.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
verify_package_integrityARead-only
[MAINTENANCE] Verify the integrity of installed package files. Detects modified, missing, or corrupted files. Only works on Arch Linux. When to use: After system crash or disk errors, verify 'linux' package files match expected checksums.
| Name | Required | Description | Default |
|---|---|---|---|
| package_name | Yes | Name of the package to verify | |
| thorough | No | Perform thorough check including file attributes. Default: false |
TDQS
Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?
Annotations declare readOnlyHint=true, which is consistent with the description. The description adds that it detects specific file issues and is limited to Arch Linux. It does not detail what occurs on failure or require privileges, but provides sufficient transparency beyond annotations.
Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.
Is the description appropriately sized, front-loaded, and free of redundancy?
Every sentence adds value: purpose, platform restriction, usage guideline. Front-loaded with [MAINTENANCE] tag. No redundant information. Very concise.
Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.
Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?
The tool has no output schema, and the description does not explain return values or error behavior. For a verification tool, this omission is notable. However, the description is adequate for an agent to understand the core functionality. Missing details on output format lower the score.
Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.
Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?
Schema description coverage is 100%, so the baseline is 3. The description mentions verifying 'linux' package files as an example but does not add significant semantic meaning beyond the schema for 'package_name' and 'thorough'.
Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.
Does the description clearly state what the tool does and how it differs from similar tools?
The description clearly states it verifies integrity of installed package files, detecting modified, missing, or corrupted files. The [MAINTENANCE] tag and specific verb-resource combination make the purpose unambiguous. It distinguishes from sibling tools by focusing on integrity verification post-crash/disk errors.
Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.
Does the description explain when to use this tool, when not to, or what alternatives exist?
Explicitly says 'When to use: After system crash or disk errors' which gives clear context. It does not specify when not to use or directly name alternatives, but the context is sufficient for an agent to decide.
Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.
Tool Schema Changelog
Recent tool additions, removals, and schema changes observed during successful MCP inspections.
44 tool updates
- Removed
analyze_package_metadata_risk - Changed
analyze_pacman_conf1 field changed- added
Input schema / properties / focusAdded value: +{ + "default": "full", + "description": "What to analyze: 'full' (all settings), 'ignored_packages' (only ignored packages), 'parallel_downloads' (only parallel downloads setting)", + "enum": [ + "full", + "ignored_packages", + "parallel_downloads" + ], + "type": "string" +}
- Removed
analyze_pkgbuild_safety - Added
analyze_storage - Added
audit_package_security - Removed
check_critical_news - Removed
check_disk_space - Removed
check_failed_services - Removed
check_ignored_packages - Removed
check_mirrorlist_health - Added
diagnose_system - Added
fetch_news - Removed
find_failed_transactions - Removed
find_package_owner - Removed
find_when_installed - Removed
get_boot_logs - Removed
get_database_sync_history - Removed
get_latest_news - Removed
get_news_since_last_update - Removed
get_pacman_cache_stats - Removed
get_parallel_downloads_setting - Removed
get_transaction_history - Removed
list_active_mirrors - Removed
list_explicit_packages - Removed
list_group_packages - Removed
list_orphan_packages - Removed
list_package_files - Removed
list_package_groups - Added
manage_groups - Added
manage_install_reason - Added
manage_orphans - Removed
mark_as_dependency - Removed
mark_as_explicit - Added
optimize_mirrors - Added
query_file_ownership - Added
query_package_history - Removed
remove_orphans - Removed
remove_package - Added
remove_packages - Removed
remove_packages_batch - Added
run_system_health_check - Removed
search_package_files - Removed
suggest_fastest_mirrors - Removed
test_mirror_speed
34 tool updates
- Added
analyze_makepkg_conf - Added
analyze_pacman_conf - Added
check_critical_news - Added
check_database_freshness - Added
check_disk_space - Added
check_failed_services - Added
check_ignored_packages - Added
check_mirrorlist_health - Added
find_failed_transactions - Added
find_package_owner - Added
find_when_installed - Added
get_boot_logs - Added
get_database_sync_history - Added
get_latest_news - Added
get_news_since_last_update - Added
get_pacman_cache_stats - Added
get_parallel_downloads_setting - Added
get_system_info - Added
get_transaction_history - Added
list_active_mirrors - Added
list_explicit_packages - Added
list_group_packages - Added
list_orphan_packages - Added
list_package_files - Added
list_package_groups - Added
mark_as_dependency - Added
mark_as_explicit - Added
remove_orphans - Added
remove_package - Added
remove_packages_batch - Added
search_package_files - Added
suggest_fastest_mirrors - Added
test_mirror_speed - Added
verify_package_integrity
7 tool updates
- First observed
analyze_package_metadata_risk - First observed
analyze_pkgbuild_safety - First observed
check_updates_dry_run - First observed
get_official_package_info - First observed
install_package_secure - First observed
search_archwiki - First observed
search_aur
TDQS
Scored across 22 tools
Each tool has a clearly distinct purpose, organized by category (CONFIG, MONITORING, LIFECYCLE, etc.). No overlapping functionality; e.g., check_updates_dry_run and run_system_health_check both involve updates but serve different roles (specific check vs. comprehensive health).
All tool names follow a consistent verb_noun or verb_phrase pattern in snake_case (e.g., analyze_makepkg_conf, install_package_secure). No mixing of conventions or vague verbs.
22 tools is appropriate for a comprehensive Arch Linux management server. Covers configuration, monitoring, lifecycle, discovery, maintenance, and organization without being excessive or sparse.
The tool set covers all major aspects of Arch Linux management: package installation/removal, updates, health checks, mirror optimization, news, wiki search, AUR security, file ownership, and package history. No obvious gaps for typical system administration tasks.
Maintenance
Related MCP Connectors
Package intelligence MCP for AI agents — 22 tools, 19 ecosystems, AGPL SDK, free.
Remote MCP for Android CLI agent build gate, structured receipts, audit logs, and reviewer-ready evi
Search GitHub, npm, PyPI, StackOverflow, ArXiv from one MCP — built for coding agents.
Personal assistant MCP server with search, execute, packages, jobs, secrets, and integrations.
Related MCP Servers
- AlicenseAqualityAmaintenanceMCP-NixOS is a Model Context Protocol server that provides real-time, accurate information about NixOS packages, options, Home Manager, and nix-darwin configurations, preventing AI assistants from hallucinating about NixOS resources and enabling them to deliver factual system configuration guidance.2830MIT
- AlicenseAqualityAmaintenanceA Model Context Protocol server that fetches up-to-date, version-specific documentation and code examples from libraries directly into LLM prompts, helping developers get accurate answers without outdated or hallucinated information.21,132,952 npm62,184MIT
- FlicenseNot gradedqualityDmaintenanceAn MCP server that retrieves and provides Wikipedia content for requested topics, enabling easy access to Wikipedia information directly through the Model Control Protocol.1-
- AlicenseNot gradedqualityDmaintenanceProvides AI-powered architecture analysis and visualization of codebases, exposing 17 MCP tools for querying components, dependencies, and generating interactive diagrams.998 npm3MIT