Glama
rajbos

GHAS MCP server (GitHub Advanced Security)

by rajbos

ghas-mcp-服务器

MCP 服务器调用 GHAS 来访问 GitHub 存储库。

目前支持以下工具:

  • list_dependabot_alerts:列出存储库的所有 dependabot 警报

  • list_secret_scanning_alerts:列出存储库的所有秘密扫描警报

  • list_code_scanning_alerts:列出存储库的所有代码扫描警报

确保将这三个范围(只读)添加到配置的 PAT 中并添加到正确的组织中!

在 VS Code 和 VS Code Insiders 中安装

使用按钮在您的 VS Code 或 VS Code Insiders 环境中安装服务器。请务必在信任之前阅读链接!链接指向vscode.dev和insiders.vscode.dev ,并包含安装服务器的说明。

VS Code 会让你在任何事情发生之前看到配置:
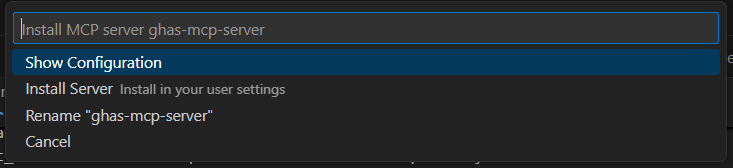
VS Code 中配置的屏幕截图

示例配置

在编辑器中将以下配置添加到您的 MCP 配置中。

安全选项:使用经过身份验证的 GitHub CLI

除了存储个人访问令牌(请参阅下一节)之外,您还可以使用经过身份验证的 GitHub CLI。这将使用您在 GitHub CLI 中配置的凭据。当您已安装 GitHub CLI 并已通过身份验证时,这非常有用。

要使用 GitHub CLI 进行身份验证,请按照以下步骤操作:

  • 将"GITHUB_PERSONAL_ACCESS_TOKEN_USE_GHCLI": "true"添加到您的环境变量中。

  • 确保您已安装 GitHub CLI,并通过运行gh auth login进行身份验证。

配置:

{
    "mcp": {
        "inputs": [
        ]
    },
    "servers": {
        "ghas-mcp-server": {
            "command": "npx",
            "args": [
                "-y",
                "@rajbos/ghas-mcp-server"
            ],
            "env": {
                "GITHUB_PERSONAL_ACCESS_TOKEN_USE_GHCLI": "true"
            }
        }
    }
  }

Related MCP server: SonarQube MCP Server

使用个人访问令牌进行配置

对于 VS Code 它看起来像这样:

{
    "mcp": {
        "inputs": [
            {
                "id": "github_personal_access_token",
                "description": "GitHub Personal Access Token",
                "type": "promptString",
                "password": true
            }
        ]
    },
    "servers": {
        "ghas-mcp-server": {
            "command": "npx",
            "args": [
                "-y",
                "@rajbos/ghas-mcp-server"
            ],
            "env": {
                "GITHUB_PERSONAL_ACCESS_TOKEN": "${input:github_personal_access_token}"
            }
        }
    }
  }

结果
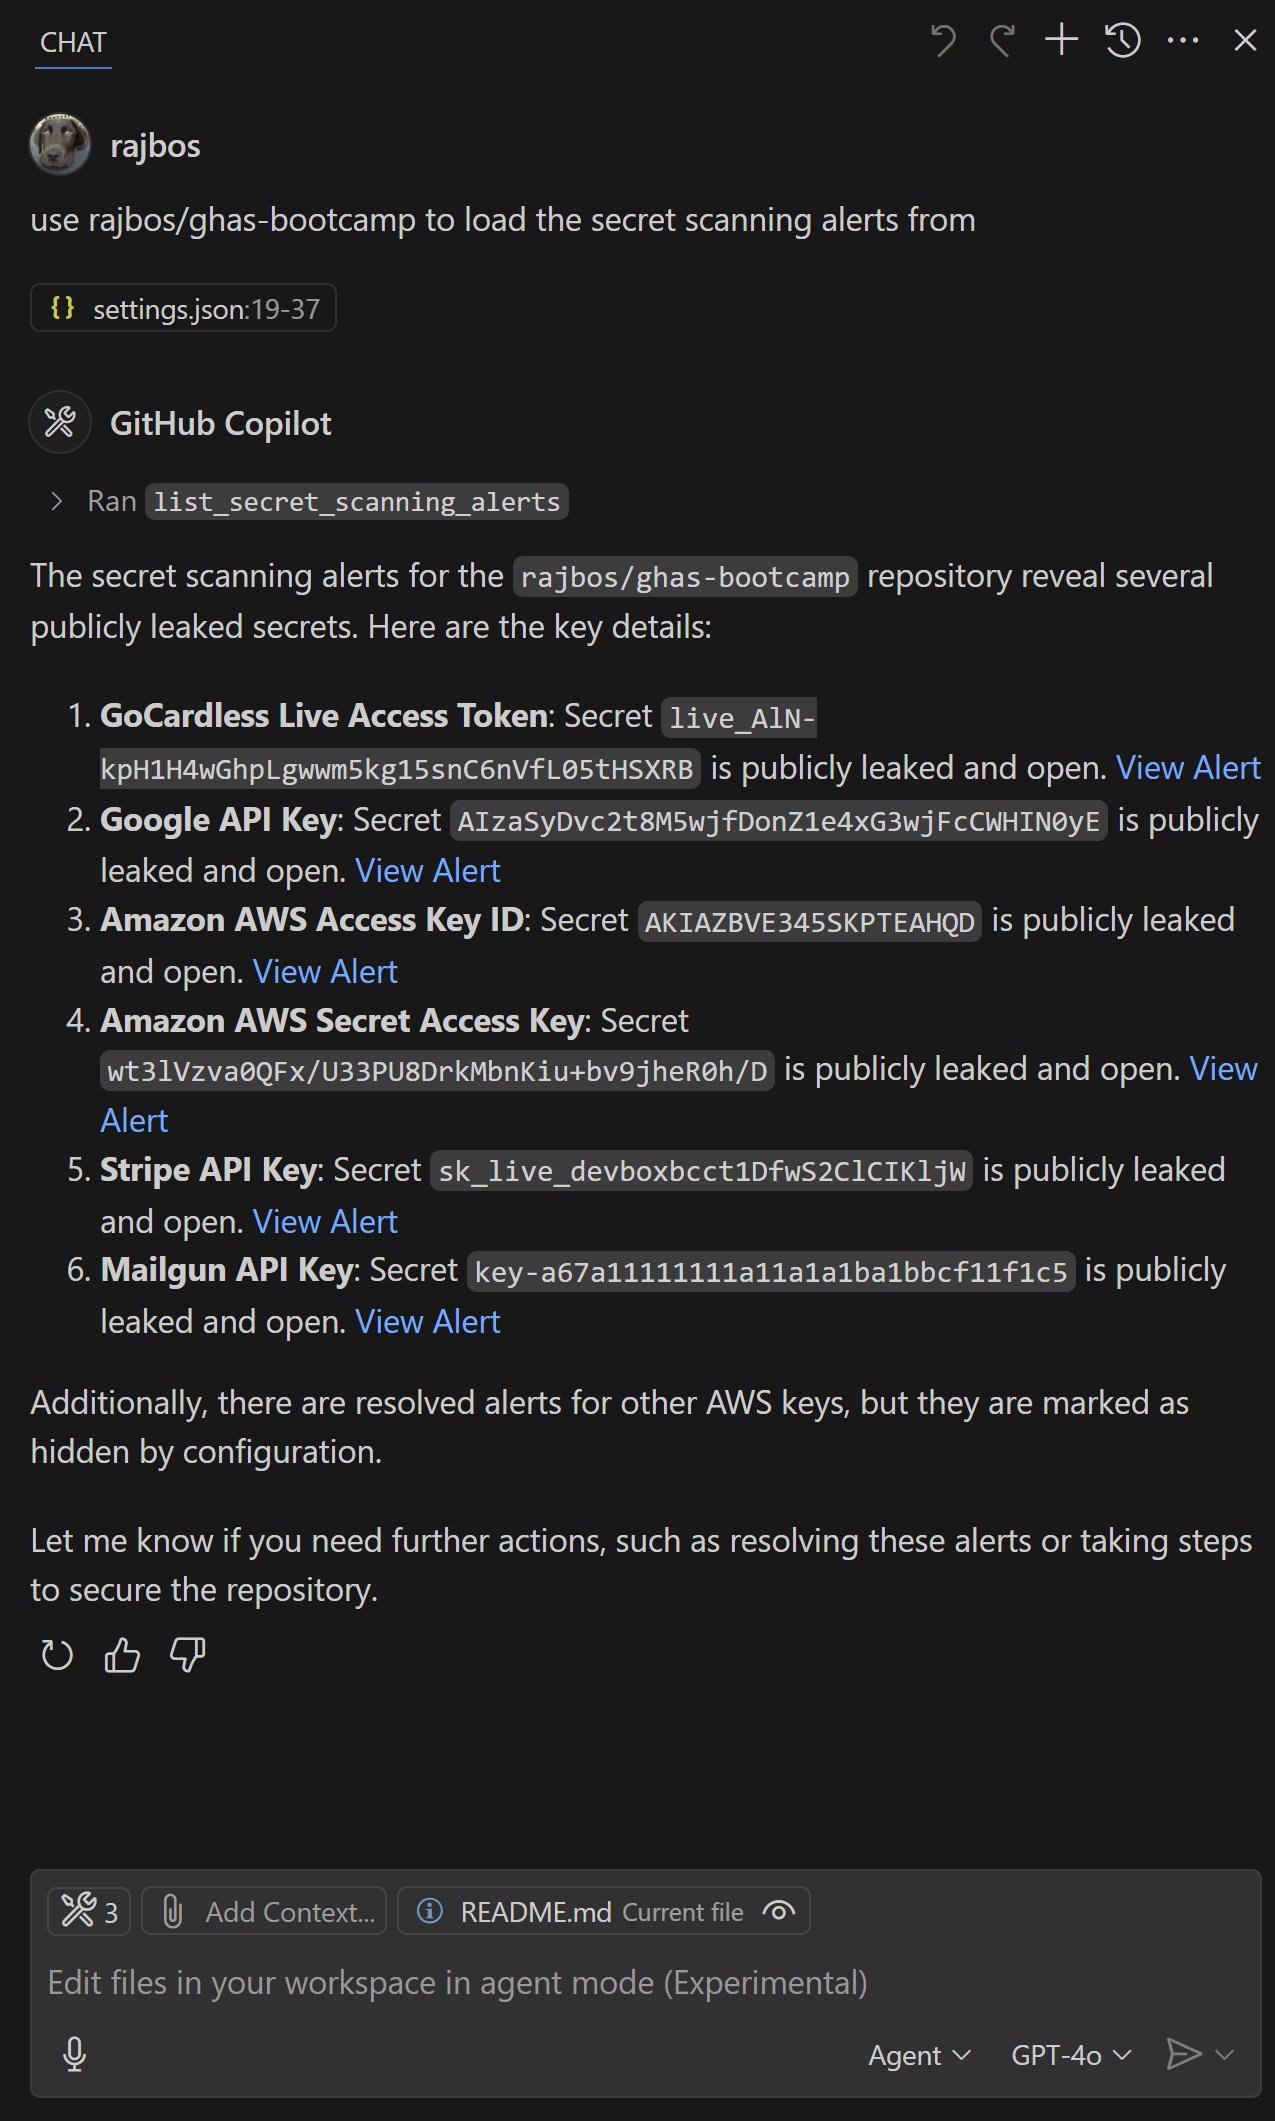
VS Code 内部输出的屏幕截图

贡献

欢迎贡献!如果您对新工具或改进有任何想法,请创建问题或提交拉取请求。

快速入门

# Install dependencies
npm install

# Build the project
npm run build

项目结构

ghas-mcp-server/
├── src/
│   ├── operations/      # MCP Tools
│   │   └── security.ts
│   └── index.ts         # Server entry point
├── package.json
└── tsconfig.json

添加组件

该项目附带src/operations/security.ts中的 GHAS 工具。

建筑

  1. 更改你的工具

  2. 运行npm run build进行编译

  3. 服务器将在启动时自动加载您的工具

测试本地构建

您可以通过使用以下 MCP 配置配置本地构建版本来测试本地构建:

"servers": {
    "ghas-mcp-server": {
        "command": "node",
        "args": [
            "C:/Users/RobBos/Code/Repos/rajbos/ghas-mpc-server/dist/index.js"
        ],
        "env": {
            "GITHUB_PERSONAL_ACCESS_TOKEN_USE_GHCLI": "true"
        }
    }
}

不要忘记先将路径更改为本地构建并构建项目!

了解更多

Available Tools

3 tools
list_code_scanning_alertsC

List the current GitHub Advanced Security code scanning alerts for a repository

ParametersJSON Schema
NameRequiredDescriptionDefault
ownerYes
repoYes

TDQS

C2.9/5.0
Behavior2/5

Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?

With no annotations provided, the description carries the full burden of behavioral disclosure. It mentions 'List the current... alerts' but does not specify whether this is a read-only operation, if it requires authentication, rate limits, pagination, or what the output format entails. This leaves significant gaps in understanding the tool's behavior.

Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.

Conciseness5/5

Is the description appropriately sized, front-loaded, and free of redundancy?

The description is a single, efficient sentence that directly states the tool's purpose without unnecessary words. It is front-loaded and appropriately sized, making it easy to parse quickly.

Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.

Completeness2/5

Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?

Given the tool's complexity (listing security alerts), lack of annotations, and no output schema, the description is incomplete. It does not cover behavioral aspects like permissions, response format, or error handling, which are crucial for effective use. The description alone is insufficient for an agent to fully understand how to invoke and interpret results.

Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.

Parameters3/5

Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?

The input schema has 0% description coverage, but the description does not add any meaning to the parameters 'owner' and 'repo' beyond implying they relate to a GitHub repository. Since there are only 2 parameters, the baseline is 4, but the description fails to compensate for the lack of schema details, such as explaining what 'owner' and 'repo' represent, resulting in a score of 3.

Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.

Purpose4/5

Does the description clearly state what the tool does and how it differs from similar tools?

The description clearly states the verb ('List') and resource ('GitHub Advanced Security code scanning alerts for a repository'), making the tool's purpose specific and understandable. However, it does not explicitly differentiate from sibling tools like 'list_dependabot_alerts' or 'list_secret_scanning_alerts', which prevents a score of 5.

Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.

Usage Guidelines2/5

Does the description explain when to use this tool, when not to, or what alternatives exist?

The description provides no guidance on when to use this tool versus alternatives, such as the sibling tools for Dependabot or secret scanning alerts. It lacks any context about prerequisites, exclusions, or specific scenarios where this tool is preferred, offering only a basic statement of function.

Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.

list_dependabot_alertsC

List the current GitHub Dependabot alerts for a repository

ParametersJSON Schema
NameRequiredDescriptionDefault
ownerYes
repoYes

TDQS

C2.9/5.0
Behavior2/5

Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?

No annotations are provided, so the description carries the full burden of behavioral disclosure. It states the tool lists alerts but does not describe key behaviors like whether it requires authentication, rate limits, pagination, or what the output format looks like. For a tool with zero annotation coverage, this lack of detail is a significant gap, warranting a score of 2.

Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.

Conciseness5/5

Is the description appropriately sized, front-loaded, and free of redundancy?

The description is a single, efficient sentence: 'List the current GitHub Dependabot alerts for a repository.' It is front-loaded with the core action and resource, with no wasted words or unnecessary details. This makes it highly concise and well-structured, earning a score of 5.

Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.

Completeness2/5

Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?

Given the tool's complexity (listing security alerts), lack of annotations, and no output schema, the description is incomplete. It does not cover behavioral aspects like authentication needs, rate limits, or output format, which are crucial for an AI agent to use the tool effectively. With these gaps, the description falls short of being fully helpful, resulting in a score of 2.

Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.

Parameters3/5

Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?

The input schema has 2 parameters (owner and repo) with 0% description coverage, meaning the schema provides no semantic details. The description does not add any parameter-specific information, such as explaining what 'owner' and 'repo' refer to or their expected formats. Since the description does not compensate for the low schema coverage, the baseline score of 3 is applied, as it neither adds value nor fully addresses the gap.

Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.

Purpose4/5

Does the description clearly state what the tool does and how it differs from similar tools?

The description clearly states the tool's purpose: 'List the current GitHub Dependabot alerts for a repository.' It specifies the verb ('List'), resource ('GitHub Dependabot alerts'), and scope ('for a repository'), which is specific and actionable. However, it does not explicitly differentiate from sibling tools like 'list_code_scanning_alerts' or 'list_secret_scanning_alerts', which reduces the score from a 5 to a 4.

Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.

Usage Guidelines2/5

Does the description explain when to use this tool, when not to, or what alternatives exist?

The description provides no guidance on when to use this tool versus alternatives. It does not mention sibling tools or any context for choosing this tool over others, such as for dependency-related security issues. Without explicit usage instructions or exclusions, the score is a 2, as it offers minimal guidance beyond the basic purpose.

Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.

list_secret_scanning_alertsC

List the current GitHub Advanced Security secret scanning alerts for a repository

ParametersJSON Schema
NameRequiredDescriptionDefault
ownerYes
repoYes

TDQS

C2.8/5.0
Behavior2/5

Does the description disclose side effects, auth requirements, rate limits, or destructive behavior?

With no annotations provided, the description carries the full burden of behavioral disclosure. It states the tool lists alerts but does not describe key traits like whether it requires authentication, has rate limits, returns paginated results, or what the output format is. This leaves significant gaps in understanding how the tool behaves.

Agents need to know what a tool does to the world before calling it. Descriptions should go beyond structured annotations to explain consequences.

Conciseness5/5

Is the description appropriately sized, front-loaded, and free of redundancy?

The description is a single, clear sentence that efficiently conveys the core purpose without unnecessary words. It is appropriately sized and front-loaded, making it easy to understand at a glance.

Shorter descriptions cost fewer tokens and are easier for agents to parse. Every sentence should earn its place.

Completeness2/5

Given the tool's complexity, does the description cover enough for an agent to succeed on first attempt?

Given the tool's complexity (listing security alerts), lack of annotations, no output schema, and low parameter schema coverage, the description is incomplete. It does not provide enough context on behavior, output, or parameter usage, making it inadequate for effective tool invocation.

Complex tools with many parameters or behaviors need more documentation. Simple tools need less. This dimension scales expectations accordingly.

Parameters2/5

Does the description clarify parameter syntax, constraints, interactions, or defaults beyond what the schema provides?

The input schema has 2 parameters with 0% description coverage, so the schema provides no semantic information. The description does not add any meaning to the parameters (owner, repo), such as explaining what they represent or how to format them, failing to compensate for the low schema coverage.

Input schemas describe structure but not intent. Descriptions should explain non-obvious parameter relationships and valid value ranges.

Purpose4/5

Does the description clearly state what the tool does and how it differs from similar tools?

The description clearly states the action ('List') and the resource ('GitHub Advanced Security secret scanning alerts for a repository'), making the purpose specific and understandable. However, it does not explicitly differentiate from sibling tools like 'list_code_scanning_alerts' or 'list_dependabot_alerts', which would be needed for a score of 5.

Agents choose between tools based on descriptions. A clear purpose with a specific verb and resource helps agents select the right tool.

Usage Guidelines2/5

Does the description explain when to use this tool, when not to, or what alternatives exist?

The description provides no guidance on when to use this tool versus alternatives, such as the sibling tools listed. It mentions the context ('for a repository') but lacks explicit when/when-not instructions or comparisons to other alert-listing tools, leaving usage unclear.

Agents often have multiple tools that could apply. Explicit usage guidance like "use X instead of Y when Z" prevents misuse.

Tool Schema Changelog

Recent tool additions, removals, and schema changes observed during successful MCP inspections.

  1. 3 tool updatesv1.0.0
    • First observedlist_code_scanning_alerts
    • First observedlist_dependabot_alerts
    • First observedlist_secret_scanning_alerts

TDQS

B3.2/5.0

Scored across 3 tools

Disambiguation5/5

Each tool has a clearly distinct purpose targeting different types of GitHub Advanced Security alerts: code scanning, Dependabot, and secret scanning. The descriptions explicitly differentiate the alert types, leaving no ambiguity about which tool to use for each security domain.

Naming Consistency5/5

All tools follow a perfect verb_noun pattern with 'list_' prefix followed by the specific alert type (code_scanning_alerts, dependabot_alerts, secret_scanning_alerts). The naming is completely consistent across all three tools with no deviations in style or structure.

Tool Count3/5

With only 3 tools, the server feels quite thin for GitHub Advanced Security's scope, which includes multiple security domains and potential operations beyond just listing alerts. While the tools cover the core alert types, the count is borderline minimal for what could be a more comprehensive security management interface.

Completeness2/5

The toolset is severely incomplete for GitHub Advanced Security operations. While it covers listing three types of alerts, there are significant gaps: no ability to create, update, dismiss, or resolve alerts; no access to security overviews or metrics; and no coverage of other GHAS features like code scanning analyses or security advisories. This creates dead ends for agents needing to take action on security findings.

Maintenance

ActivityInactive
ResponsivenessNo issues

Related MCP Connectors

Related MCP Servers

  • A
    license
    A
    quality
    Not graded
    maintenance
    Enterprise-grade MCP (Model Context Protocol) server for detecting secrets and sensitive information in GitHub repositories. Scans for 35+ types of secrets including API keys, passwords, tokens, and credentials with production-ready reliability features.
    5
    0
    -
  • A
    license
    A
    quality
    B
    maintenance
    MCP server for Cursor that scans codebases for security issues including hardcoded secrets, SAST, vulnerable dependencies, and IaC misconfigurations.
    7
    MIT
  • F
    license
    A
    quality
    D
    maintenance
    Enables searching and analyzing CVEs and vulnerabilities from multiple sources, optimized for PR review scenarios to help developers identify the latest security issues.
    8
    2
    -